SOC 2 Type 1 vs Type 2: What It Means for Hiring Software
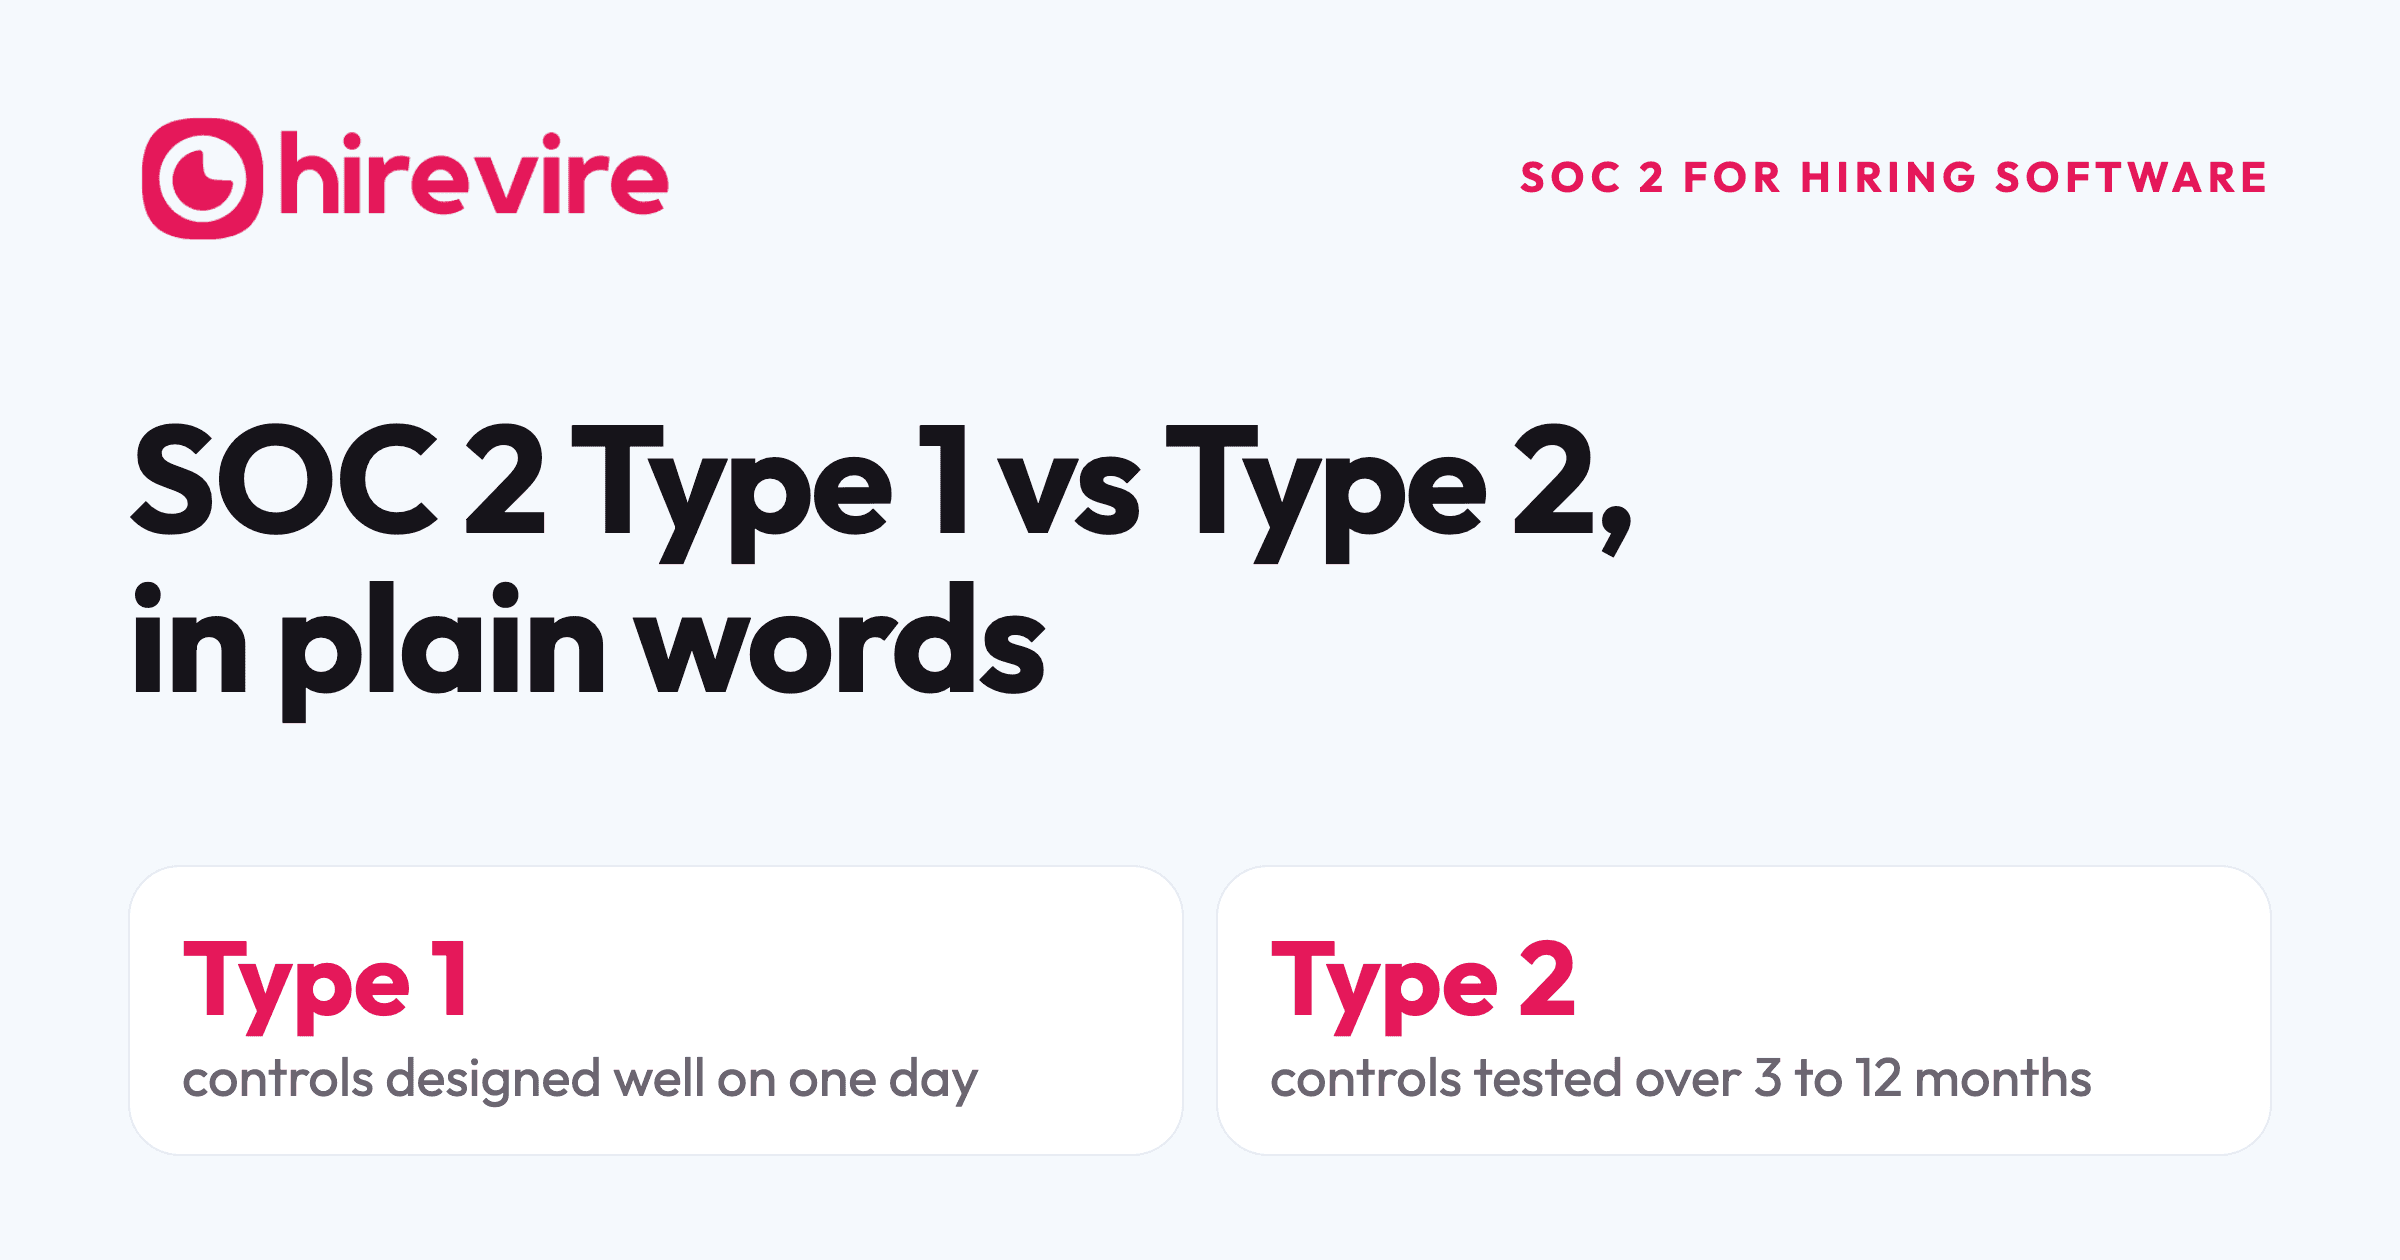
SOC 2 Type 1 checks that a vendor's security controls were designed properly on one day. SOC 2 Type 2 tests that those same controls actually worked, every day, over a period of three to twelve months. That is the whole SOC 2 Type 1 vs Type 2 difference, and it is why security teams treat a Type 2 report as proof and a Type 1 report as a promise. If you are comparing hiring tools while you read, you can try Hirevire free for 7 days, no credit card needed.
Picture a hiring tool that holds 4,000 candidate videos. A Type 1 report says the vendor has a rule that deletes videos after 90 days. A Type 2 report says an auditor picked a sample of days across six months and confirmed the deletion actually ran. For anyone who has to answer to a candidate, a client or a regulator, the second sentence is the one that counts.
SOC 2 Type 1 vs Type 2: what is the difference?
Type 1 looks at the design of a vendor's controls at a single point in time. Type 2 looks at the design and then tests whether the controls operated over a stretch of months. Both are reports written by an independent CPA firm under rules set by the AICPA.
| SOC 2 Type 1 | SOC 2 Type 2 | |
|---|---|---|
| What the auditor checks | Controls exist and are designed well | Controls exist, are designed well and worked over time |
| Time covered | One date | Usually 3 to 12 months |
| Testing | Reads policies, looks at settings | Samples real evidence across the period: tickets, access logs, deletion records |
| Typical time to get one | A few weeks after controls are in place | The observation period plus a few weeks of fieldwork |
| What it tells a buyer | The vendor has a security program | The security program runs every day |
| How security teams read it | A first step | The standard most reviews ask for |
A vendor usually earns Type 1 first, then starts the observation window for Type 2. So a Type 1 report on its own often means a young security program, which is normal for a newer company and fine to accept with a few extra questions.
What does a SOC 2 Type 2 report actually test?
A SOC 2 Type 2 report tests the controls a vendor chose under the AICPA Trust Services Criteria, across the full observation period. Security is required in every SOC 2 report. Availability, processing integrity, confidentiality and privacy are optional and the vendor picks which to include.
In practice the auditor pulls samples. For a hiring tool that might mean 25 new employees checked for background screening and security training, every user removed in the period checked for same-day access removal, a set of code changes checked for review and approval, and backup restore tests checked for dates and results.
Each control gets one of two outcomes: tested with no exceptions, or tested with exceptions. An exception means the auditor found at least one case where the control did not work, such as a former contractor who kept access for two weeks. Exceptions are common and usually sit in Section 4 of the report, usually with the vendor's response. Read that section first.
Is SOC 2 a certification?
SOC 2 is an attestation report, so strictly speaking nobody is "SOC 2 certified". A licensed CPA firm gives an opinion on the vendor's controls, and the vendor shares the report, usually under an NDA. Marketing pages often say "SOC 2 certified" or "SOC 2 compliant" as shorthand, which is fine in everyday talk.
What matters for a buyer is the wording on the report itself: which type, which criteria, which dates and which audit firm. Ask for the report, check those four details, and the label on the website stops mattering.
What does Type 1 vs Type 2 mean for candidate video data?
For candidate video, Type 2 is the report that shows the controls around recordings held up for months in a row. A one-way video tool stores faces, voices, CVs, transcripts and AI scores for people outside your company, and three controls protect most of that data.
- Access. Who inside the vendor can open a candidate's video, and is that access removed when they leave? Type 1 shows the access policy. Type 2 shows the auditor checked real leavers.
- Deletion. Does the retention rule actually delete videos on schedule? Type 1 shows the rule is set up. Type 2 shows it ran across the period.
- Change control. Did every update to the product go through review before release? A bad release can expose recordings, so Type 2 sampling of real changes matters here.
For recruiting agencies the stakes are higher, because a client's security team will review the tools the agency uses to hold the client's candidates. A Type 2 report answers that client in one document. The page on video screening for recruitment agencies shows how client sharing works day to day.
What should you ask a vendor that only has Type 1 or says "in progress"?
Ask four questions, in writing, and keep the answers with your review. A vendor with Type 1 or an audit in progress can still be a good choice when the answers are clear.
- When does the Type 2 observation period start and end, and which audit firm is doing it?
- Can you see the Type 1 report now, or a readiness letter from the auditor?
- Which Trust Services Criteria will the Type 2 cover? Security only, or also confidentiality and privacy?
- How long are candidate videos kept, and can the vendor confirm a deletion in writing?
"In progress" with no auditor name or dates is a sales answer. Treat it as no report yet, and lean harder on the data processing agreement and the security questionnaire. The guide to a vendor security assessment for a video interview tool lists every document to collect and the order the review runs in.
How long is a SOC 2 Type 2 report valid?
A SOC 2 Type 2 report is generally treated as current for 12 months after its period ends, because most vendors renew it every year. The report itself has no expiry date. Your security team decides how old is too old.
When the period ended more than about three months ago, ask for a bridge letter. It is a short signed note from the vendor that says nothing material has changed in its controls since the period closed, and it covers the gap until the next report arrives.
Where does Hirevire stand on SOC 2 Type 2?
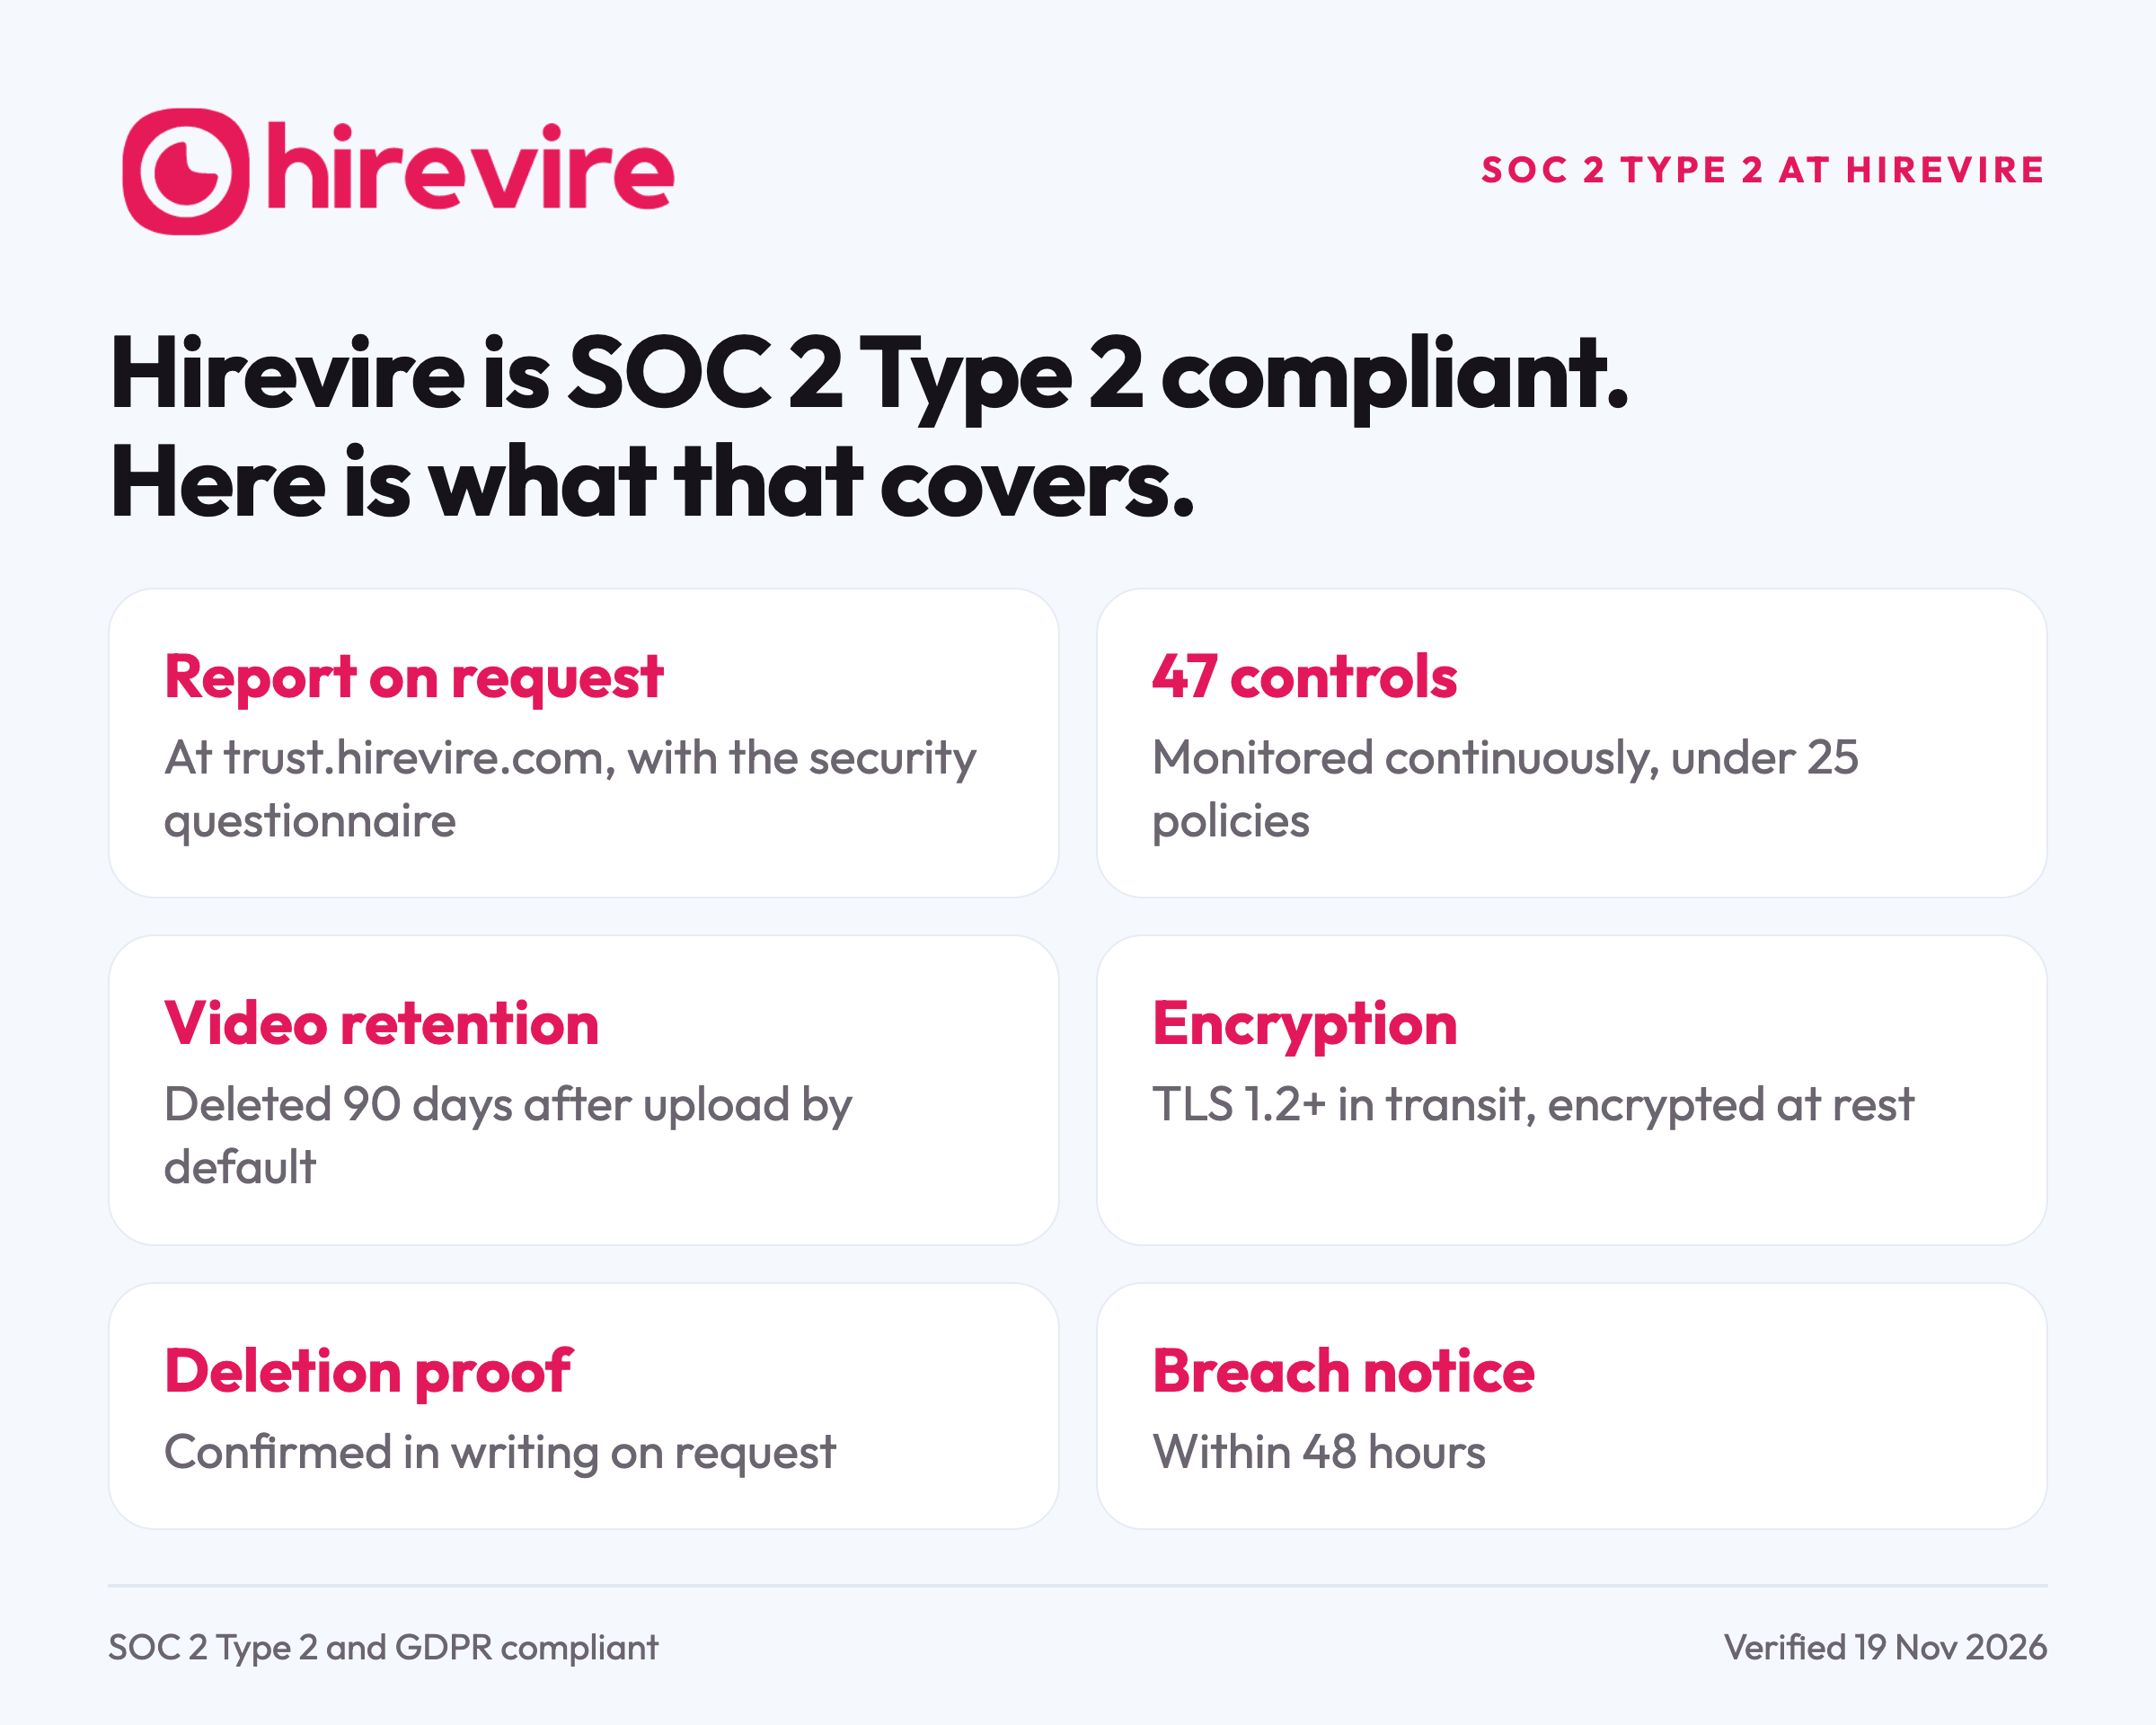
Hirevire is SOC 2 Type 2 compliant, and the Hirevire Trust Center lists it alongside GDPR, with 25 policies and 47 continuously monitored controls. Your security team can request the report and fill in the security questionnaire on the Trust Center.
Hirevire is one-way video screening software for small teams and recruiting agencies. You write the questions and send one link, and candidates record answers in their browser with no account and no app. Every answer is transcribed by AI in 90+ languages, and AI scorecards rate each response against your criteria, with the reasoning shown. Both come on every plan, which starts at $468 a year on the pricing page.
The data controls a security team asks about are written into the Hirevire DPA:
| Control | What Hirevire does |
|---|---|
| Encryption | TLS 1.2+ in transit; encrypted at rest across database, object storage and media storage |
| Video retention | Kept 90 days from upload by default, then deleted within 30 days; longer storage can be bought |
| Backups | Deleted data ages out of backups within 7 days |
| Deletion proof | Written confirmation of deletion on request |
| Breach notice | Within 48 hours of Hirevire becoming aware of it |
| Shared links | Shared review links carry an expiry date and an optional password |
Webhooks, Zapier and Make pass screened candidates to your ATS or calendar tool, so the review covers one screening tool and the rest of your stack stays as it is. To see it with your own questions before security signs off, try Hirevire free for 7 days, no credit card needed.
Watch how Hirevire screens candidates from one link. Then send the Trust Center link to your security team, and if the tool fits your hiring, try Hirevire free for 7 days, no credit card needed.
For the rest of the same buying decision, the list of SOC 2 Type II video interview platforms shows which tools hold a report and how to get it, and the GDPR compliant recruiting software comparison covers the privacy side.
Frequently asked questions
Is SOC 2 Type 2 better than Type 1?
Type 2 gives a buyer more assurance, because an auditor tested the controls over months. Type 1 confirms the controls were designed well on one date. Most security teams ask for Type 2 and accept Type 1 from newer vendors with a dated plan for Type 2.
How long does a SOC 2 Type 2 audit take?
The observation period runs 3 to 12 months, and the auditor's fieldwork and report add a few more weeks. A vendor going from no report to its first Type 2 usually needs six months to a year.
What is the difference between SOC 1 and SOC 2?
SOC 1 covers controls that affect a customer's financial reporting, such as a payroll processor. SOC 2 covers security and, where included, availability, processing integrity, confidentiality and privacy. A hiring tool that stores candidate data should have SOC 2. Both come in Type 1 and Type 2.
Can you see a vendor's SOC 2 report?
Yes, as a customer or a serious prospect. Vendors share the full report under an NDA, often through a trust center. A shorter SOC 3 report is sometimes public, but it leaves out the control tests and exceptions that a security team needs.
Does SOC 2 cover GDPR?
No. SOC 2 is a US attestation on security controls. GDPR duties such as lawful basis, candidate notices and deletion requests sit in the data processing agreement and the privacy policy, so legal teams ask for those alongside the SOC 2 report.
Is Hirevire SOC 2 Type 2 compliant?
Yes. The Hirevire Trust Center at trust.hirevire.com lists SOC 2 Type 2 and GDPR as compliant, with 25 policies and 47 monitored controls. Security teams can request the report and complete the security questionnaire there.