Vendor Security Assessment for a Video Interview Tool
A vendor security assessment for a video interview tool asks for four things: the vendor's SOC 2 Type II report, a data map of what candidate data the tool holds and where, the list of sub-processors, and the retention and deletion terms. Send all four in your first email to the security team, with the vendor's DPA and a filled security questionnaire, and the review starts with everything on the table. If you are still choosing a tool, you can try Hirevire free for 7 days, no credit card needed, while the review runs.
Picture the usual week. You found a one-way video tool that saves your team ten hours of phone screens, the hiring manager loves it, and then procurement replies with a 200-row spreadsheet. This guide shows what that spreadsheet is really asking, the order the review runs in, and what to send for a tool that records candidates on video.
What does a vendor security assessment ask for?
A vendor security assessment asks the vendor to prove four things: that its controls are audited, what data it holds, who else touches that data, and when the data is deleted. Every questionnaire format comes back to those four.
| What security asks for | The question behind it | Where it usually lives |
|---|---|---|
| SOC 2 Type II report | Has an auditor tested the vendor's controls over months? | Vendor trust center, shared under NDA |
| Data map | What candidate data goes in, and where is it stored? | DPA annex or security overview |
| Sub-processor list | Which other companies process the data, and in which country? | DPA annex or a public sub-processor page |
| Retention and deletion | How long are videos kept, and how is deletion confirmed? | DPA and privacy policy |
SOC 2 Type II report
This is an independent CPA firm's report on whether the vendor's security controls worked over a period, usually 3 to 12 months. Security teams ask for Type II because a Type I report only checks the design on one day. The guide to SOC 2 Type 1 vs Type 2 covers the difference in plain words. If the audit period ended more than a few months ago, ask the vendor for a bridge letter, a short signed note that says nothing material changed since the period closed.
Data map
Security wants a plain list of the personal data the tool collects: names, emails, phone numbers, CVs, video and audio, transcripts, AI scores and reviewer comments. Next to each item they want the storage location and the country.
Sub-processor list
A sub-processor is any company the vendor uses to process your candidates' data, such as a cloud database or a video delivery network. Under GDPR Article 28, the vendor has to tell you who they are and give you a chance to object when the list changes.
Retention and deletion
For a video tool, this is the question that matters most to legal. How many days are videos kept by default, can you delete a candidate on request, and does deletion reach backups?
How does a vendor security review run, step by step?
A vendor security review runs in five steps: intake, risk tiering, questionnaire, document review and contract. The times below are common ranges for a small SaaS tool that holds candidate data. A large bank or a public body can take longer at every step.
- Intake form (1 to 3 days). You describe the tool, who uses it and what data it touches. Say "candidate video, audio and CVs" up front, because security will find out anyway.
- Risk tiering (a few days). Security sorts the vendor into low, medium or high risk. A tool holding personal data on hundreds of outside people usually lands in medium or high, which means the full questionnaire.
- Security questionnaire (1 to 2 weeks). The vendor fills in a standard form such as the SIG Lite from Shared Assessments, the CAIQ from the Cloud Security Alliance, or your company's own spreadsheet. Vendors with a trust center often answer this in a day.
- Document review (about 1 week). Security reads the SOC 2 report, checks the audit period dates and reads the exceptions section. Zero exceptions is the goal, and any exception should come with a written fix.
- DPA and contract (about 1 week). Legal signs or reviews the data processing agreement, checks the sub-processor list and the breach notice time, and approves.
The slowest part of most reviews is waiting for documents. A recruiter who sends the full pack on day one can cut the questionnaire and document steps down to days.
Why does a video interview tool get a closer look?
A video interview tool gets a closer look because it records faces and voices of people outside your company. A candidate's video can reveal age, ethnicity, a disability or religion, and GDPR Article 9 treats that kind of data with extra care even when nobody asked for it.
Three details raise the stakes for a one-way video tool:
- Candidates are outsiders. They never signed your employee privacy notice, so the vendor's handling of their data is all they have.
- Reviewers share videos. A hiring manager forwarding a link to a client or a panel moves candidate data outside the tool.
- AI may score answers. Security and legal will ask whether AI makes or only supports the hiring decision, and which AI provider sees the transcripts.
Expect questions on all three, and answer them before they are asked.
What should you send for a one-way video interview tool?
Send one email with seven items: the SOC 2 report request link, the data map, the sub-processor list, the retention terms, the AI processing terms, the access controls for shared links, and the breach notice time. Each answers a row the reviewer would otherwise chase.
- The SOC 2 Type II report, or the link where security can request it under NDA, plus a bridge letter if the period is old.
- The data map: the categories of candidate data and where each is stored.
- The sub-processor list with countries and transfer safeguards.
- Retention: how long videos stay by default and how deletion works.
- AI use: which provider processes transcripts, whether it trains on them, and whether AI scores are advisory.
- Access controls: user roles inside the workspace, plus expiry and password options on shared review links.
- Breach notification: how many hours after discovery the vendor tells you.
For an agency, add one line on how client hiring managers see candidates. Clients often run their own review of the tools an agency uses, so the same pack answers both. The page on video screening for recruitment agencies shows how client sharing works day to day.
What is in a vendor security questionnaire?
A vendor security questionnaire is a standard list of yes or no and short-answer questions about the vendor's security program. Most companies send the SIG Lite, the CAIQ or their own spreadsheet, and the questions repeat across all three.
Common sections are access control, encryption, incident response, business continuity, staff background checks, change management, sub-processors and data retention. A SOC 2 Type II report already covers most of these, which is why many security teams accept the report plus a short custom form in place of the full questionnaire. Ask your security team whether that shortcut is allowed before the vendor spends a week on 300 rows.
How does Hirevire answer a security review?
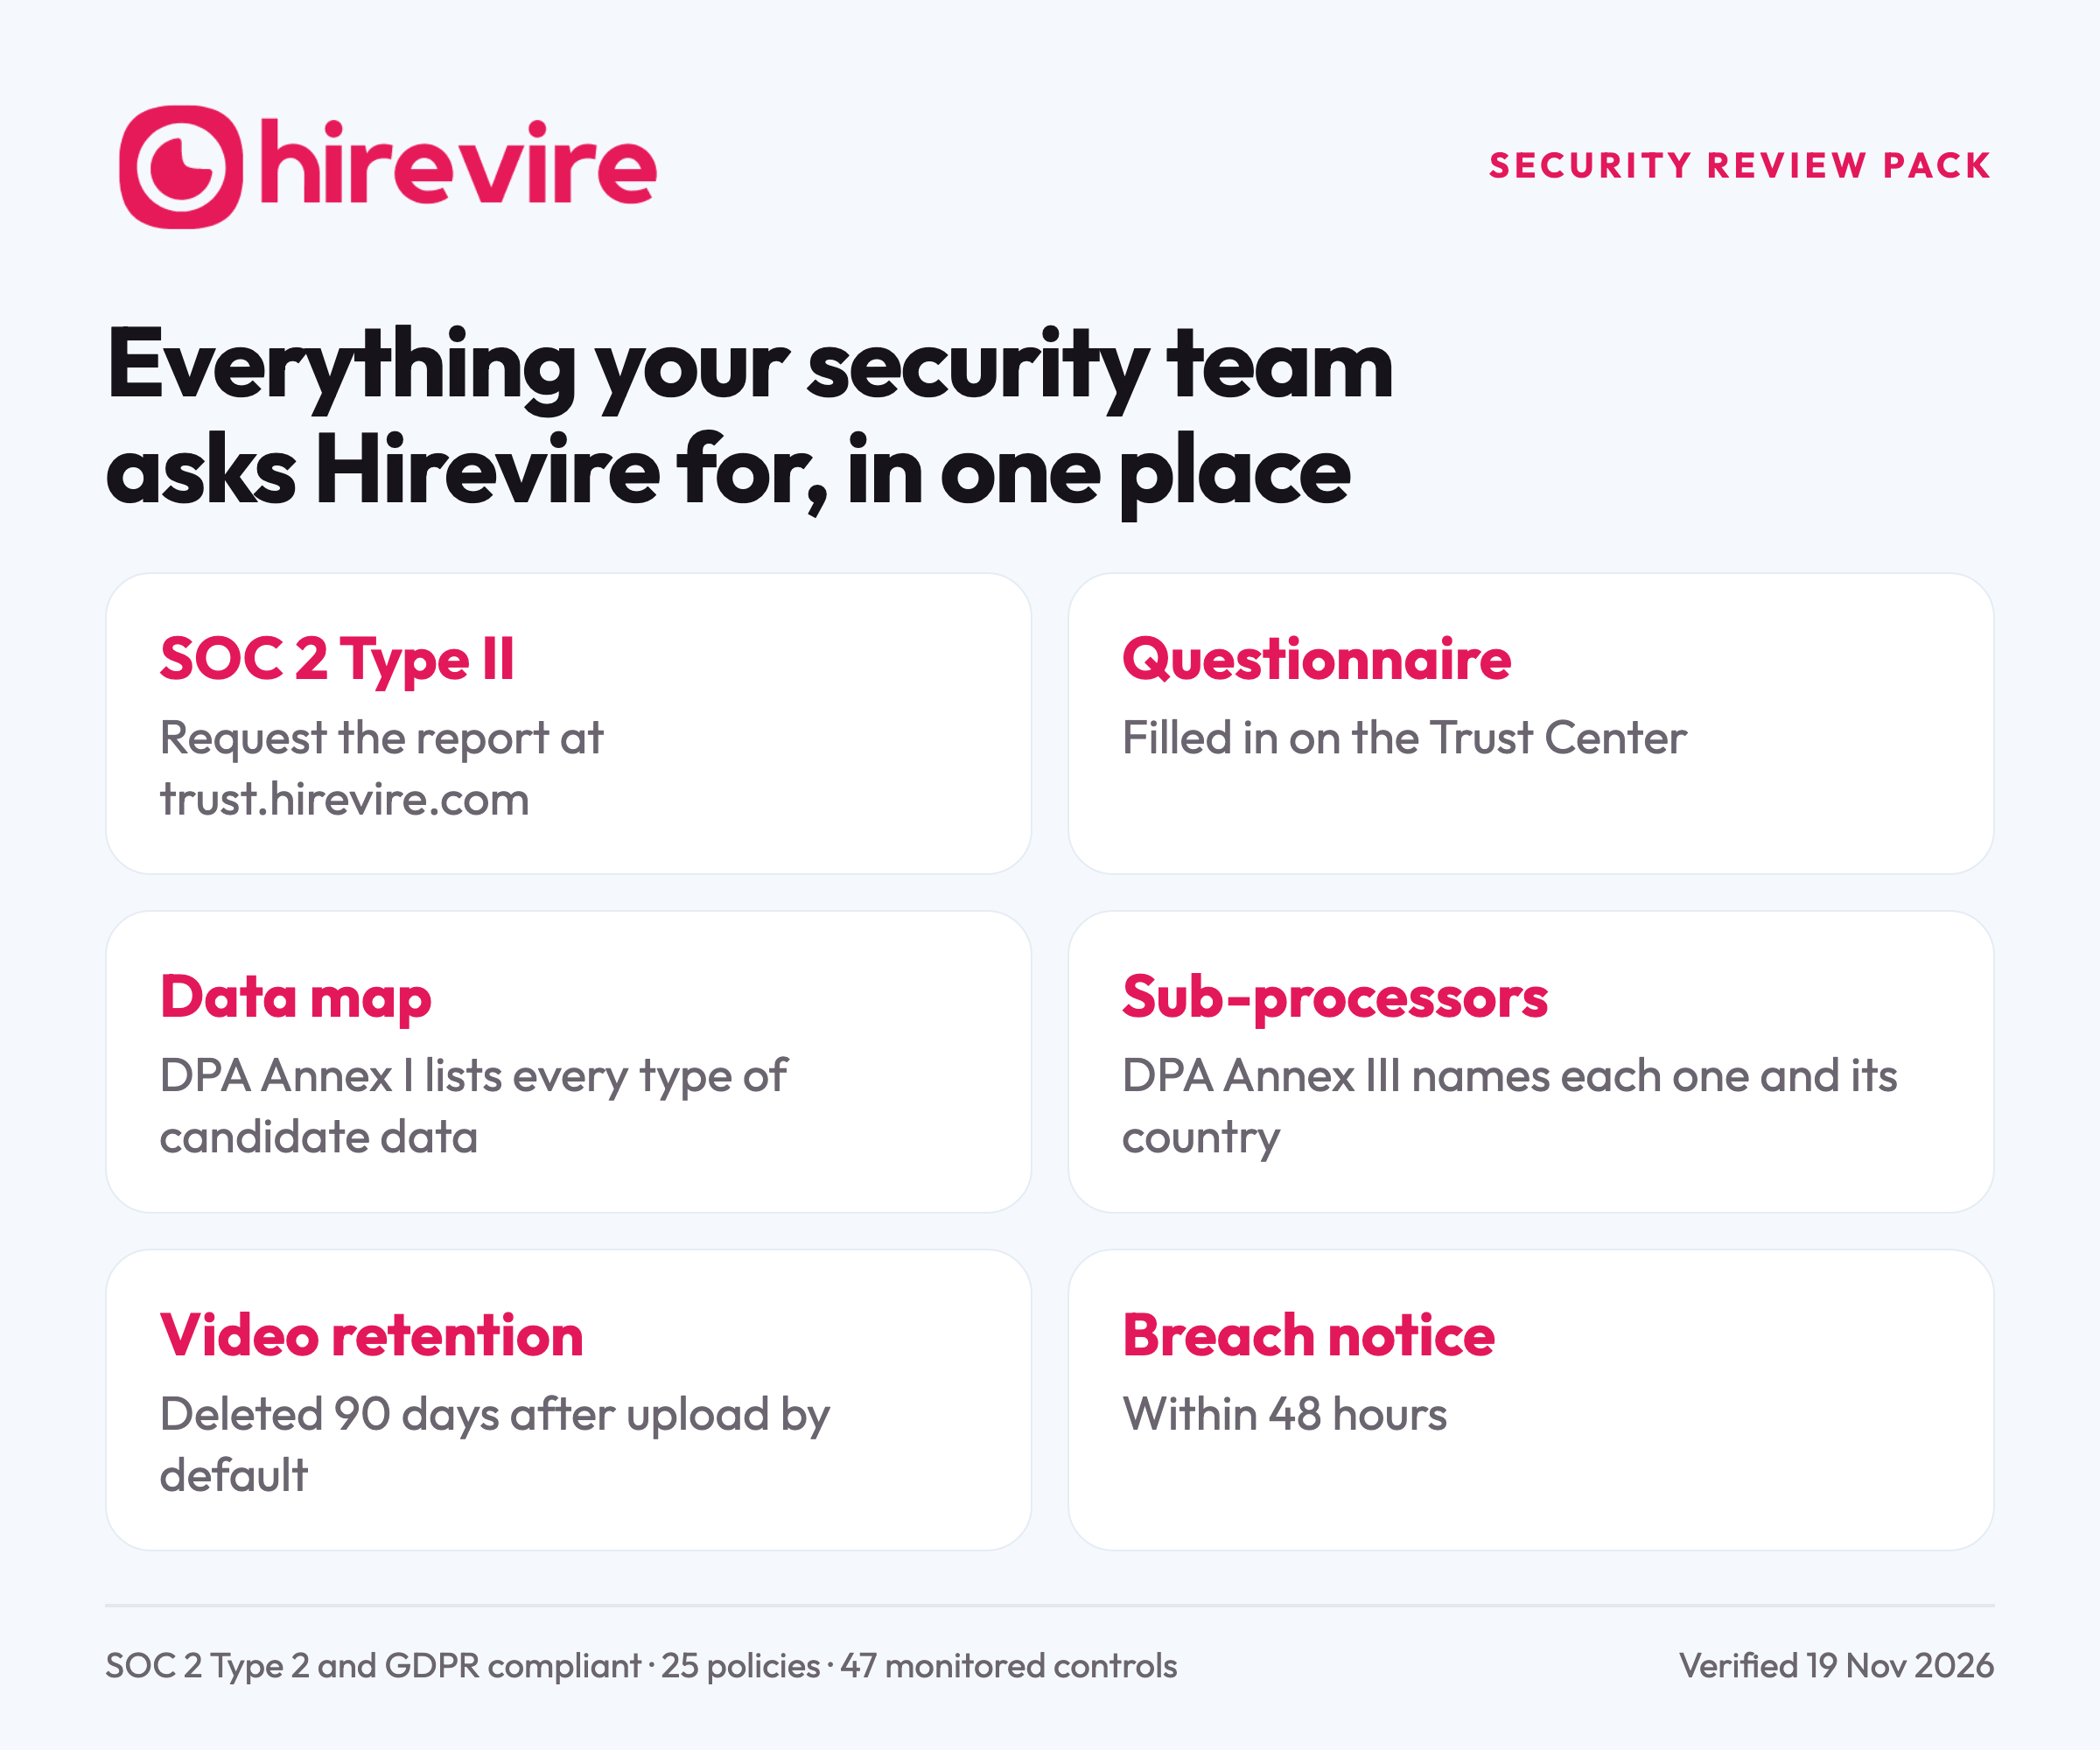
Hirevire answers a security review from one place: the Hirevire Trust Center, which lists SOC 2 Type 2 and GDPR as compliant.
Hirevire is one-way video screening software for small teams and recruiting agencies. You write the questions and send one link, and candidates record answers in their browser with no account and no app. Every answer is transcribed by AI in 90+ languages, and AI scorecards rate each response against your criteria, with the reasoning shown. Both come on every plan, which starts at $468 a year on the pricing page.
Each item in the pack maps to a page Hirevire already publishes.
| Security asks for | Where Hirevire answers it |
|---|---|
| SOC 2 Type II report | Request access at trust.hirevire.com, which shows 25 policies and 47 continuously monitored controls |
| Security questionnaire | Filled in on the Trust Center |
| Data map | Annex I of the DPA lists every category of candidate data |
| Sub-processors | Annex III of the DPA names each one with its location and transfer safeguard |
| Retention | Videos and audio kept 90 days from upload by default, then deleted within 30 days; backups age out within 7 days; longer storage can be bought |
| Breach notice | Within 48 hours of Hirevire becoming aware of it |
Two details tend to close the conversation with security. AI scoring is opt-in per workspace and its output is advisory, so a person always makes the decision; transcripts sent for scoring go to OpenAI under Zero Data Retention, and transcription runs on Cloudflare Workers AI, which does not train on customer data. Shared review links carry an expiry, an optional password and a noindex tag, so a link forwarded to a client stops working on the date you set.
Webhooks, Zapier and Make pass screened candidates on to your ATS or calendar tool, and the DPA treats those as destinations you choose. The review covers one small tool, and the rest of your stack stays as it is. To see it with your own questions before security signs off, try Hirevire free for 7 days, no credit card needed.
How do you write the email to your security team?
Write a short email that names the tool, the data it touches and the links to every document, so security can start on the same day. A version you can copy:
Subject: Security review request: Hirevire (one-way video screening)
We want to use Hirevire to screen candidates for the customer support role. Candidates record video answers in their browser; the tool stores their name, email, CV, video, audio, transcripts and our reviewers' ratings.
SOC 2 Type II report and security questionnaire: trust.hirevire.com DPA with data map (Annex I) and sub-processors (Annex III): hirevire.com/dpa Privacy policy: hirevire.com/privacy-policy Retention: candidate video deleted 90 days after upload by default. AI scoring: opt-in and advisory; transcripts processed under Zero Data Retention.
We would like to start a pilot on 1 December. Which form should we fill in next?
The last line matters. It gives security a date and asks for their process, which gets a faster reply than "please approve".
Watch how Hirevire screens candidates from one link, then send the pack above to security. If it fits your hiring, try Hirevire free for 7 days, no credit card needed.
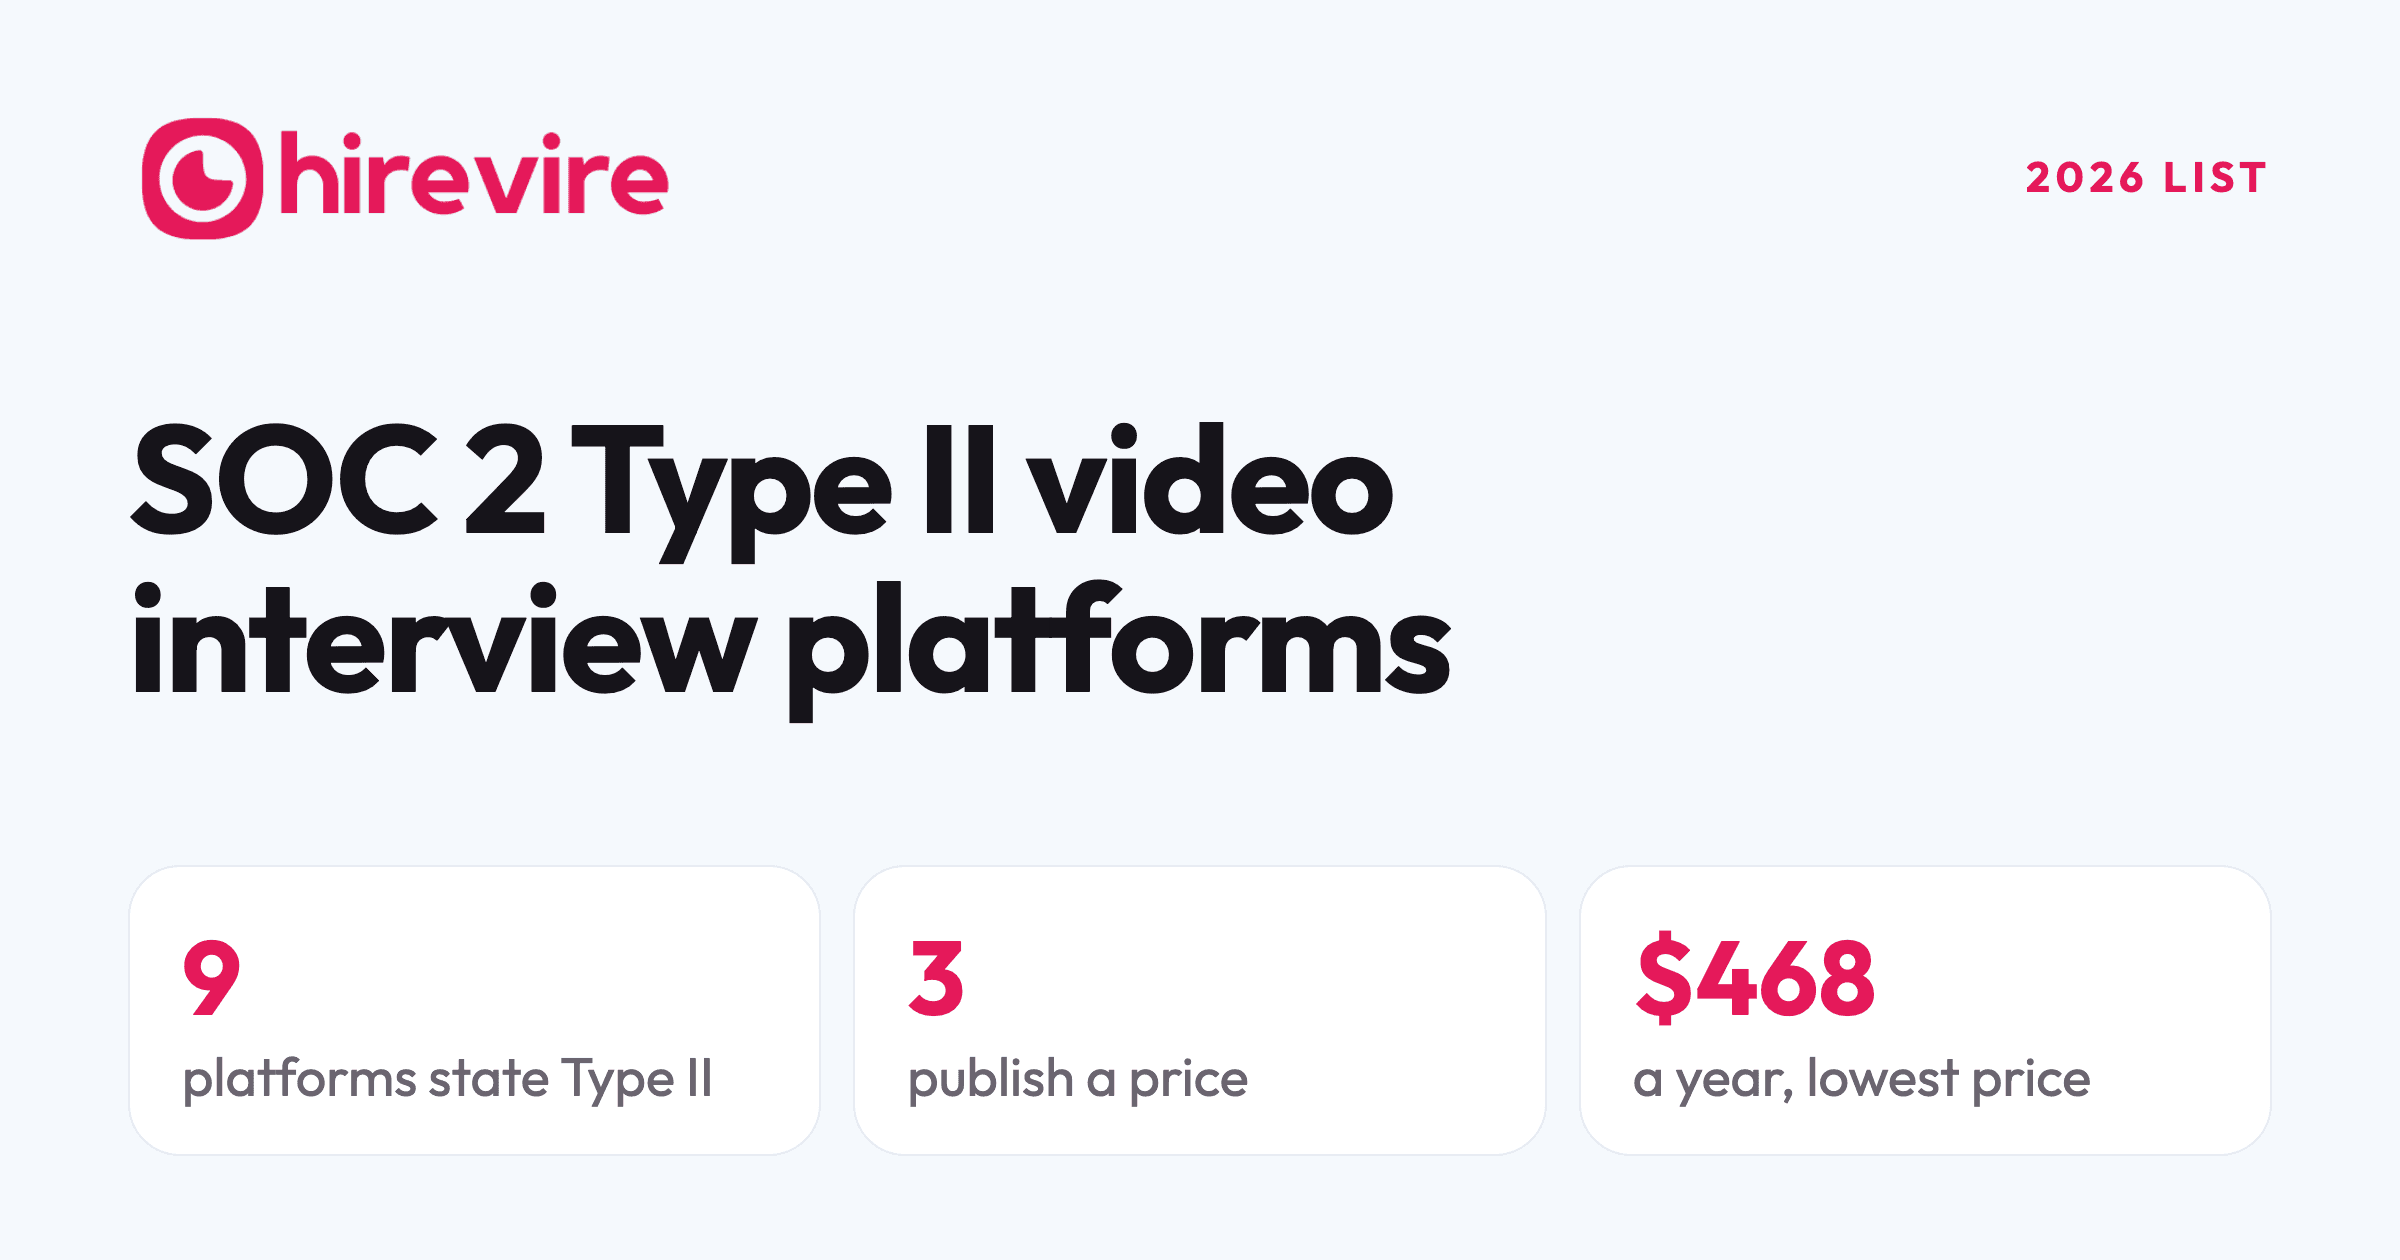
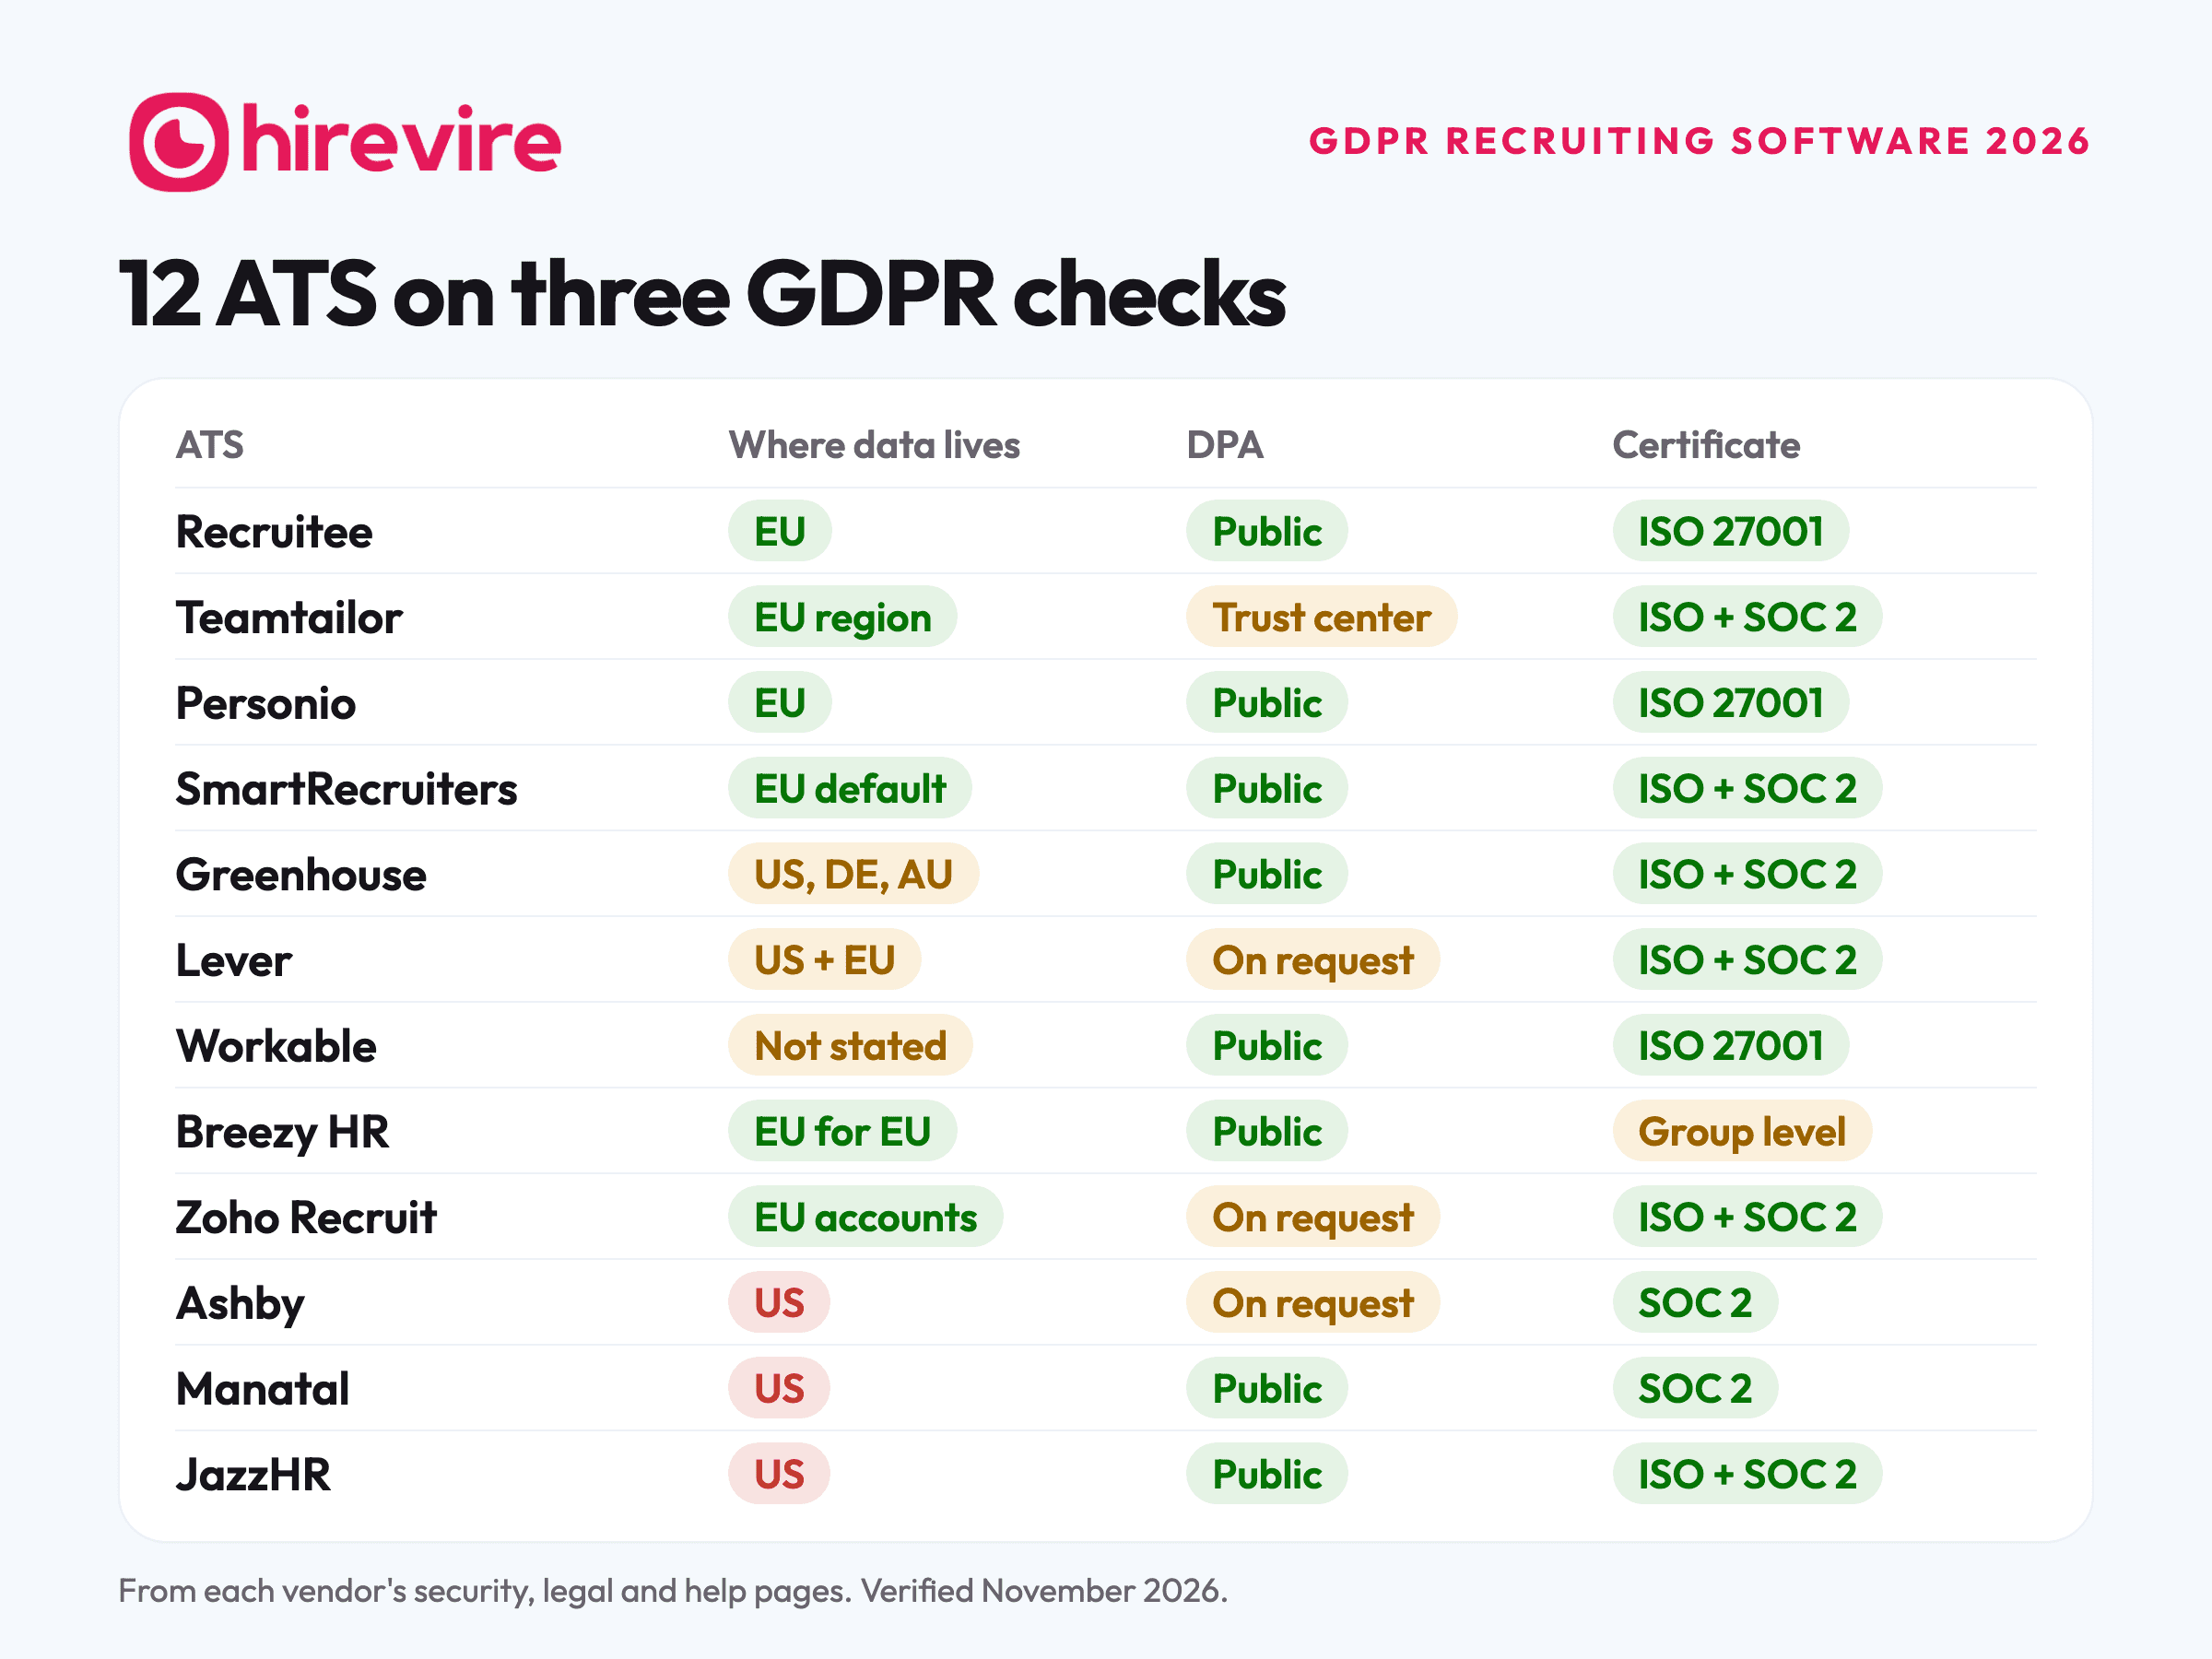
For the next steps in the same review, the list of SOC 2 Type II video interview platforms compares who holds a report and how to get it, the GDPR compliant recruiting software comparison covers the privacy side, and the guide to compliant AI hiring covers AI scoring rules.
Frequently asked questions
What is a vendor security assessment?
A vendor security assessment is the review your security team runs before a new tool can touch company or candidate data. It checks the vendor's audited controls, the data it holds, its sub-processors and its retention terms, and ends with an approve, approve with conditions, or reject.
How long does a vendor security review take?
Most reviews of a small SaaS tool take three to five weeks from intake to signed DPA. Sending the SOC 2 report, DPA, sub-processor list and questionnaire answers on day one removes most of the waiting.
What is a SOC 2 bridge letter?
A bridge letter is a short signed statement from the vendor covering the gap between the end of its last SOC 2 audit period and today. It says no material change happened to its controls in that gap. Ask for one when the report's period ended more than about three months ago.
Is a SOC 2 report enough for a vendor security assessment?
A SOC 2 Type II report covers most of the security questions, so many teams accept it with a short custom form. Legal still needs the DPA, the sub-processor list and the retention terms, because SOC 2 does not cover GDPR duties.
What does a vendor security questionnaire include?
It covers access control, encryption, incident response, business continuity, staff screening, change management, sub-processors and data retention. Common formats are the SIG Lite, the CAIQ and company-made spreadsheets.
Does Hirevire have a SOC 2 Type II report?
Yes. The Hirevire Trust Center at trust.hirevire.com lists SOC 2 Type 2 and GDPR as compliant, with 25 policies and 47 monitored controls, and your security team can request the documents and fill the security questionnaire there.
Sources
- Hirevire Trust Center
- Hirevire Data Processing Agreement
- Hirevire Privacy Policy
- Hirevire pricing
- AICPA: SOC 2 reporting
- Shared Assessments: Standardized Information Gathering (SIG) questionnaire
- Cloud Security Alliance: STAR registry and CAIQ
- GDPR Article 28: Processor
- GDPR Article 9: Special categories of personal data